
SD-WAN solved a real problem, but it is not the full answer to where enterprise networking is headed. It gave enterprises a policy-driven way to use MPLS, Internet and other transports more flexibly, including direct cloud access where appropriate. For the underlying architecture choice, see our guide to modern enterprise WAN architecture.
Why SD-WAN Is Still Part of the Future
It isn’t anymore. Enterprise networking has moved past “just connectivity.” Today’s networks need to secure a distributed workforce and protect cloud application access. They also need to carry AI workloads, whose network requirements vary significantly by use case. That combination pushed the industry toward a more converged, intelligent architecture. It also changed the future of enterprise networking beyond what SD-WAN alone was built to handle.
Gartner’s definition of SASE captures this shift well. Gartner coined the term Secure Access Service Edge in 2019. It described a cloud-delivered architecture that merges networking and security into one system. Zero Trust increasingly anchors the security side of that architecture. NIST’s Zero Trust Architecture publication formalizes those principles. The framework influences how modern SASE platforms verify users and devices.
This guide follows that evolution from MPLS to SD-WAN and then to SASE. It explains what SASE includes and where AI fits into the picture. It also highlights what enterprises should assess before choosing a migration path. If your next step is MPLS-to-SD-WAN, use our SD-WAN migration checklist. It covers assessment, pilot, cutover, and validation. Our guides on SD-WAN vs Traditional WAN and what SASE actually is provide the foundations. This article connects those pieces into the larger picture of the future of enterprise networking.
This shift matters for practical reasons, not just technical ones. IT budgets and security posture depend on network performance. Employee productivity does too, especially as work becomes more distributed.
Quick Answer: What’s Beyond SD-WAN?
Yes, SD-WAN remains part of the future of enterprise networking. Increasingly, it serves as the connectivity foundation for a broader architecture. That architecture combines SASE or SSE, Zero Trust, automation, and AI-assisted operations. SD-WAN still optimizes how traffic moves. The next stage secures, observes, and automates that connectivity as one adaptive system. For the component-level view of edges, planes, overlays and traffic flow, see our SD-WAN architecture guide.
Put simply, SD-WAN answers: “How does traffic get where it needs to go?” SASE answers: “How do we secure that traffic wherever the user is?” AI adds a third question: “How can we make those decisions faster and smarter?” Together, these three layers describe the future of enterprise networking. They also point toward the direction the industry is likely to keep taking.
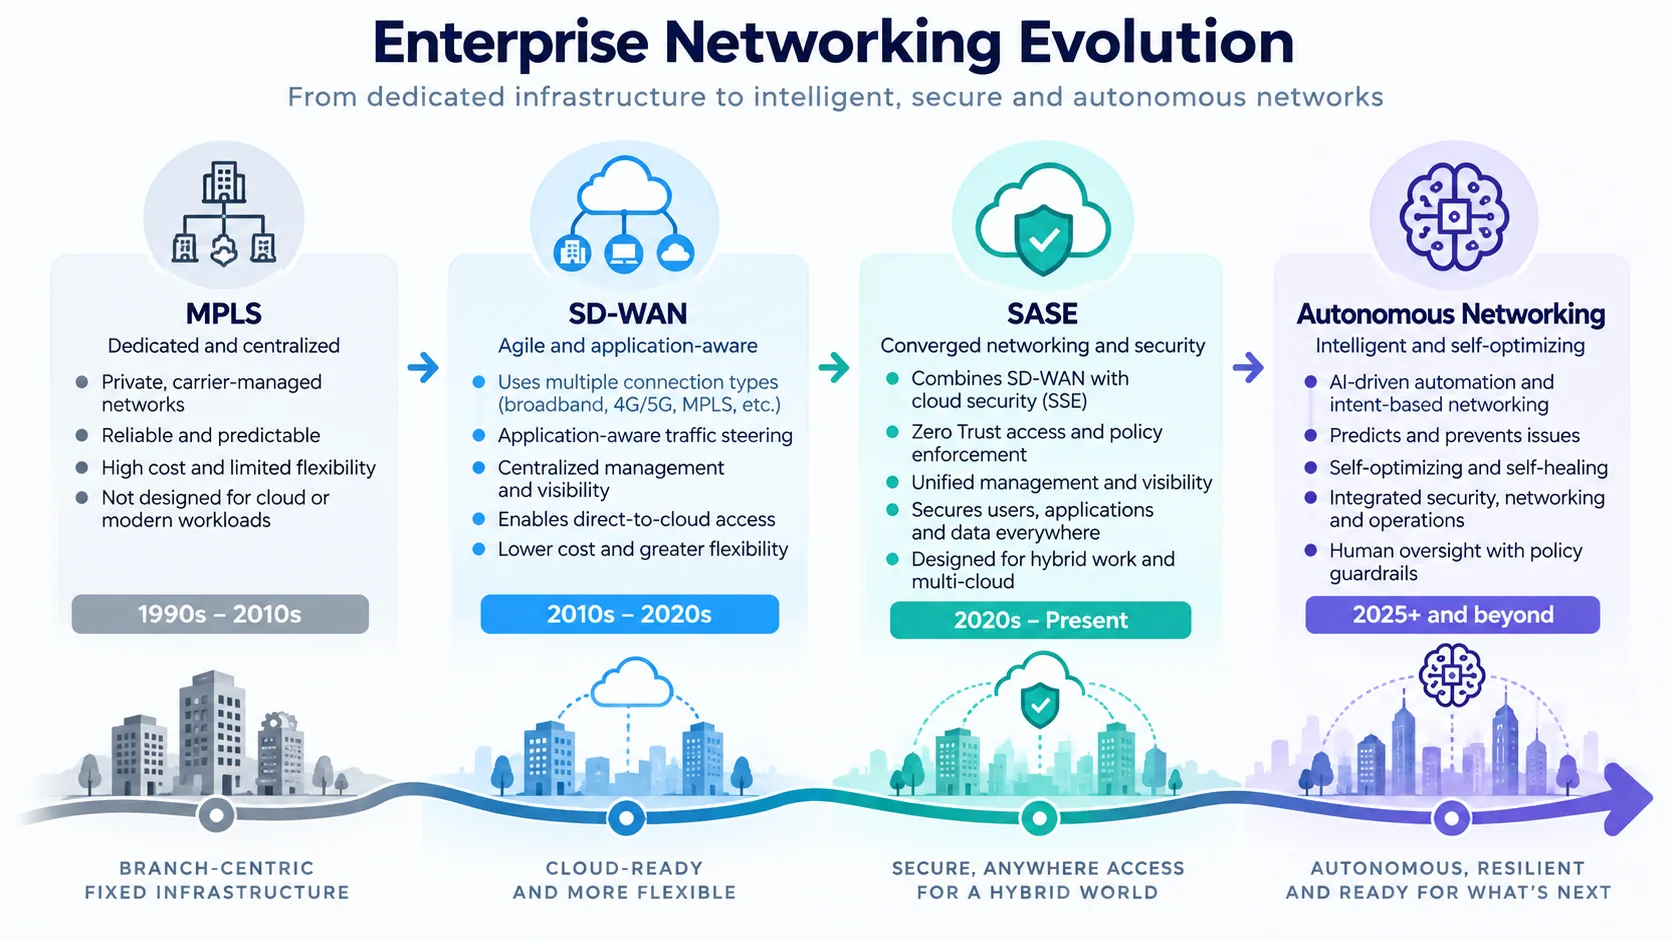
A Brief History: From MPLS to SD-WAN to SASE
The MPLS Era
For years, enterprises relied on MPLS circuits to connect branch offices to a central data center. MPLS offered reliable, predictable performance. But it came with real costs. Circuits were expensive. Adding a new site took weeks or months. And every piece of traffic, even traffic headed to a cloud application, had to backhaul through the data center first.
This model made sense when most applications lived in the data center. It made less sense once companies adopted Salesforce, Microsoft 365, and many other cloud services. A simple email check could require an unnecessary round trip through central infrastructure. The network no longer matched how the applications themselves worked.
The SD-WAN Era
SD-WAN changed the equation. Instead of relying on one expensive MPLS circuit, SD-WAN let companies use multiple connection types, broadband, LTE, MPLS, together, and dynamically chose the best path for each type of traffic. It also allowed direct-to-cloud breakout, letting branch traffic reach cloud applications without detouring through a central hub first.
This delivered real savings and performance gains. Companies could add a new branch office in days instead of months. Broadband circuits did not require the same lengthy provisioning process as MPLS. Our guide on SD-WAN vs Traditional WAN explains why this was such a major improvement. The pressures discussed in is MPLS dead? also pushed many companies to modernize. That shift laid the groundwork for what came next. SD-WAN’s software-defined foundation made a security-focused convergence like SASE technically feasible.
The SASE Era
SD-WAN solved connectivity. It didn’t fully solve security. Companies bolted on firewalls, secure web gateways, and other point products to cover that gap, often from several different vendors. That patchwork created its own problems: inconsistent policy enforcement, fragmented visibility, and a growing list of dashboards for IT teams to manage separately.
Each additional security vendor also meant another contract to negotiate, another support relationship to maintain, and another set of logs that didn’t automatically correlate with the others. Security teams often found themselves manually piecing together an incident timeline across three or four different systems just to understand what actually happened during a breach.
In 2019, Gartner introduced SASE as a converged architecture. It combines SD-WAN with cloud-delivered security under a shared policy model. The shift has gained momentum since then. Gartner projected that 60% of new SD-WAN purchases would be bundled into single-vendor SASE offerings by 2026. That compares with 15% in 2022. The change reflects growing demand for a simpler alternative to fragmented network and security stacks.
Why SD-WAN Alone Isn’t Enough for the Future of Enterprise Networking
Two forces broke the old SD-WAN-only model.
First, the workforce spread out. Remote and hybrid work moved users beyond the branch office. They now connect from homes, coffee shops, airports, and many other locations. Traditional SD-WAN was built mainly to optimize traffic between fixed sites. That model does not map cleanly to highly mobile users.
Second, separate security products create real friction around SD-WAN. Each vendor adds another policy, dashboard, and possible configuration gap. Enterprises need consistent protection for users and traffic. That protection should work regardless of location. A growing patchwork of point products makes that consistency harder to achieve.
A third factor also played a role: the sheer volume and diversity of cloud applications. A typical mid-size enterprise may rely on dozens of SaaS tools across HR, finance, sales, and engineering. Each tool brings its own access requirements. Managing that sprawl through a purely SD-WAN-centric lens quickly becomes difficult at scale. The challenge grows without a unified security layer. Even disciplined organizations often discover that their real SaaS footprint is much larger than leadership expected.
If you’re still working through the fundamentals of SD-WAN itself before diving into what comes next, our What Is SD-WAN guide is a good starting point.
Where SASE Fits After SD-WAN
SASE is the next architectural layer in this evolution. It brings SD-WAN connectivity together with cloud-delivered security and Zero Trust principles. For the detailed architecture and component breakdown, see our SASE guide. For a direct decision-oriented comparison, use SD-WAN vs SASE. Here, the focus is on what that convergence means for the future of enterprise networking.
SASE isn’t one single product. It’s a combination of several components working together under one architecture, unified by a shared policy engine rather than operating as separate, disconnected tools.
SD-WAN (the networking foundation)
SD-WAN remains the networking layer inside SASE. It still handles intelligent path selection and connectivity between sites, but now as one piece of a larger, security-integrated system, rather than standing alone as its own separate solution.
SWG (Secure Web Gateway)
A Secure Web Gateway inspects web traffic and enforces acceptable-use policies, blocking malicious sites and risky downloads before they reach the user, no matter which device or location that traffic originates from.
CASB (Cloud Access Security Broker)
A CASB gives visibility and control over how employees use cloud applications, helping enforce data protection policies across sanctioned and unsanctioned SaaS tools alike, including the “shadow IT” tools employees adopt without formal approval.
ZTNA (Zero Trust Network Access)
ZTNA replaces the old model of broad network access with granular, identity-based access to specific applications. We’ll cover this in more depth in the Zero Trust section below.
FWaaS (Firewall-as-a-Service)
Firewall-as-a-Service delivers firewall protection from the cloud rather than a physical appliance, applying consistent policy no matter where traffic originates, and removing the need to maintain and patch physical firewall hardware at every individual site.
For a deeper breakdown, our What Is Secure Access Service Edge (SASE) guide covers the architecture in more detail. This article provides the conceptual overview. The dedicated SASE guide goes deeper into deployment models, vendor considerations, and rollout planning.
How SASE Works
SASE steers traffic intelligently to the nearest cloud edge point of presence, rather than backhauling it to a central data center. Security inspection then happens right there, close to the user, cutting the latency that a longer backhaul route would otherwise add.
Policy enforcement shifts too. SASE does not trust a user simply because they are on the corporate network. Instead, policy is based on identity, device posture, and context. A user on an unmanaged device from an unfamiliar location may receive tighter restrictions. The same user on a corporate laptop inside a known office may receive broader access.
This context-aware approach also adapts in real time. If a user’s device posture changes mid-session, say, a security patch falls out of date, or the device connects from an unusual location, the system can reassess and adjust access accordingly, rather than relying on a single, one-time check performed only at login.
Single-Vendor SASE vs Multi-Vendor (Unified) SASE
Once an organization decides to pursue SASE, a real decision follows: single-vendor or multi-vendor.
Single-vendor SASE means one provider delivers the full stack. That includes SD-WAN and the security suite under one management console. This can reduce complexity because teams use one policy engine and one data model. Troubleshooting also happens in one place. Traffic may also avoid extra hops between different vendors’ cloud platforms.
Multi-vendor, or best-of-breed, SASE combines separate SD-WAN and security vendors. This gives a company more flexibility when choosing products. The trade-off is greater operational complexity. IT teams must replicate and synchronize policies across multiple systems. Troubleshooting may also require coordination with more than one vendor.
Gartner’s guidance highlights the potential of single-vendor SASE to reduce complexity, cost, and latency. The market is still maturing, however. Feature depth and integration quality vary between providers. That makes careful vendor evaluation especially important.
The decision often comes down to organizational priorities. A company that values simplicity may prefer single-vendor SASE. This is especially true for lean IT teams. Larger enterprises may prefer a multi-vendor model instead. They may already have dedicated networking and security specialists. They may also accept more integration work in exchange for greater product choice.
For readers still comparing older remote-access approaches against this newer model, our VPN vs SASE guide breaks down how traditional VPNs stack up against SASE specifically.
The AI Layer: How AI Is Shaping the Future of Enterprise Networking
SASE converged networking and security. AI is now changing how network decisions are made. Some choices that once required manual judgment can now be automated. This pushes enterprise networking toward more self-managing systems.
AI-Powered Path Selection
Modern SD-WAN already uses SLA measurements such as latency, jitter, and packet loss. These metrics help steer application traffic dynamically across available links. AI and AIOps add another layer by correlating larger telemetry sets. They can identify anomalies and predict degradation. In advanced implementations, they can also trigger policy changes or remediation. A video call may shift automatically when quality starts to fall. Over time, these systems can learn from historical patterns. They may anticipate congestion during predictable peak periods instead of reacting only after performance drops.
AIOps: Predictive Analytics and Self-Healing Networks
AIOps applies machine learning to network operations data. It can spot anomalies before they become outages. It can also flag unusual patterns before users start complaining. In more advanced implementations, AIOps may trigger automated remediation. Over time, the system builds a baseline for what “normal” looks like on a specific network. That baseline helps expose subtle deviations that humans may miss in raw logs. Accuracy can also improve as the system observes more traffic patterns.
AI-Driven Threat Detection
Within SASE’s security stack, AI also plays a growing role in threat detection. Distributed traffic across thousands of users and devices creates huge volumes of data. Human security teams cannot realistically monitor all of it manually. AI models can flag unusual patterns much faster. Examples include unexpected data access or a device behaving outside its normal baseline. Our AI in Cybersecurity guide explores this shift in more depth.
Supporting AI Workloads Themselves
There is a second dimension to AI’s role in networking. The network increasingly has to carry AI traffic, not just analyze it. AI workloads do not all have the same network profile. Interactive generative AI and RAG applications need responsive access. Distributed training and GPU-to-GPU traffic can require much higher bandwidth and more predictable latency. A network that cannot prioritize this traffic may slow down important applications. Application-aware QoS is therefore becoming more important in modern SD-WAN and SASE platforms.
This distinction matters more than it might first appear. Older QoS approaches prioritized traffic by broad category, such as voice, video, or general data. AI workloads do not always fit neatly into those buckets. Treating them as generic data can reduce performance. Modern platforms increasingly add AI-specific recognition to their prioritization logic. This reduces the need for teams to create custom rules for every new AI tool.
For a fuller grounding in AI itself before diving deeper into its networking applications, our Ultimate Guide to Artificial Intelligence covers the fundamentals.
Zero Trust and SASE
Zero Trust rests on a simple principle: never trust, always verify. The request location does not determine trust. This differs from older security models. In those models, being inside the corporate network or connected through a VPN often implied trust.
ZTNA puts this principle into practice. It does not grant broad network access after a single login. Instead, users receive access to specific applications. That access is continuously checked against identity, device health, and context. If something changes during a session, access can be revoked immediately.
This continuous verification marks a major shift from one-time authentication. A successful login at 9am does not guarantee trust for the rest of the day. Access continues to be evaluated throughout the session. This reduces the window of opportunity for an attacker. A stolen password alone may no longer be enough. Context checks can detect an unfamiliar device, unusual location, or unexpected behavior.
Zero Trust is not a bolt-on feature within SASE. It is foundational to how the architecture handles access. The Cloud Security Alliance’s research provides vendor-neutral context for cloud-delivered environments. For a practical reference, see NIST SP 1800-35: Implementing a Zero Trust Architecture. Finalized in 2025, it documents implementation patterns and examples. Our What Is Cybersecurity guide covers the broader security fundamentals.
SASE and AI Use Cases
Securing the Hybrid and Remote Workforce
SASE extends consistent security policy to users wherever they connect. It replaces a patchwork of VPNs and branch-specific firewalls. A sales representative in a hotel can receive the same protection as an employee at headquarters. IT does not need a separate solution for every location.
Multi-Cloud and SaaS Application Access
Companies increasingly spread applications across multiple clouds and SaaS platforms. SASE provides one consistent way to secure and monitor that access. This reduces the need for separate policies in every cloud environment. It can be especially useful during mergers and acquisitions. Two different cloud footprints may then need a unified security approach quickly.
IoT and Edge Device Connectivity
Connected devices increase the number of endpoints a network must secure. Many cannot run traditional security agents. SASE can extend policy to those devices at the network edge. Network-level controls still apply even when the device cannot run security software. Our IoT guide explores this device landscape in more depth.
AI Workload and Data Center Interconnect
Enterprises running distributed AI training or inference need reliable traffic prioritization. Application-aware QoS can help keep those workloads responsive. This remains important when other traffic competes for the same bandwidth. Distributed AI infrastructure can also depend on predictable connectivity between data centers. Consistent performance helps those workloads operate efficiently.
Benefits of Converging SD-WAN, SASE, and AI
Bringing these three pieces together delivers real, measurable advantages:
- Unified policy management. One console and one policy engine replace a scattered collection of point-product dashboards, making consistent enforcement far easier to achieve.
- Reduced attack surface. Consistent, identity-based protection for every user closes the gaps that a patchwork of separate tools tends to leave open.
- Lower total cost of ownership. Consolidating multiple point products into one converged platform cuts licensing costs and reduces the operational overhead of managing several separate systems.
- Improved application performance. AI-optimized path selection routes traffic more intelligently than static, rule-based routing ever could.
- Faster incident response. AIOps-driven automation catches and often resolves problems before they visibly affect end users.
- Simplified compliance reporting. A single policy engine generates more consistent, centralized logs, making it easier to demonstrate compliance during an audit than piecing together records from several disconnected systems.
Consolidating hardware and point products can also reduce power use and equipment footprint. Our Sustainable IT guide explores that broader topic. For organizations tracking environmental impact, infrastructure consolidation can create measurable benefits. Those gains can sit alongside the more obvious security and performance improvements.
Challenges and Considerations
Market and Vendor Maturity
The single-vendor SASE market is still developing. Feature depth and integration quality vary between providers. Security capabilities also differ significantly. A vendor strong in networking may still be catching up in security, or vice versa. Enterprises should therefore evaluate providers carefully before making a long-term commitment.
Migration Complexity
Moving from legacy MPLS or VPN architectures to SASE is a phased journey. It is rarely a weekend cutover. Timelines vary with estate size, architecture, security requirements, and operating model. Large enterprises often migrate site by site or user group by user group. A phased rollout reduces disruption. It also lets IT teams resolve configuration issues before they affect the wider organization.
Interoperability in Multi-Vendor Environments
Organizations that choose a multi-vendor approach face real interoperability friction. Policies in one vendor’s system do not automatically sync with another’s. IT teams may need to replicate changes across platforms. That process becomes difficult to scale manually. Automation and infrastructure-as-code practices can help. Our DevOps guide covers those principles in more detail.
Skills and Operational Readiness
Network teams need new skills to run a converged SASE environment well. These include cloud security fundamentals and identity and access management. Teams also need to work effectively with AI-driven operations tools. Relying only on manual monitoring is no longer enough. Organizations that underinvest in retraining may struggle to get full value from the platform.
How to Evaluate Whether Your Organization Is Ready
A few questions help clarify whether a SASE migration makes sense right now:
- How distributed is your workforce, and how much of your traffic currently backhauls unnecessarily through a central location?
- How much of your application footprint already lives in the cloud, versus on-premises?
- What’s your current MPLS or legacy WAN cost burden, and how much of that could shift toward a more flexible model?
- Do you face compliance requirements, like CMMC, HIPAA, or PCI DSS, that would benefit from centralized, consistent policy enforcement?
- Does your IT team have the bandwidth to manage a phased migration, or would a more gradual, department-by-department rollout fit your operational capacity better?
Answering these questions honestly helps set realistic expectations. SASE is not automatically the right next step for every organization. A company with mostly on-premises applications may see less immediate benefit than a cloud-first business. The assessment should include both networking and security teams. Their combined input can surface priorities that a narrower technical review may miss.
15-Minute Enterprise Networking Modernization Review
Before committing to a major WAN or SASE program, use one short review to identify the next sensible step.
- Minutes 0–3 — Business and application change: identify where users and applications now operate compared with when the current WAN was designed.
- Minutes 3–6 — Current friction: note measurable problems such as unnecessary backhaul, inconsistent security policy, slow branch deployment, limited visibility, or repeated manual operations.
- Minutes 6–9 — Architecture gap: decide whether the main gap is connectivity, security convergence, remote-user access, observability, or operational automation.
- Minutes 9–12 — Readiness: check skills, operating model, security governance, migration capacity, and whether the organization can support the target architecture after deployment.
- Minutes 12–15 — Next action: choose one evidence-based step and assign an owner, success measure, and review date.
The outcome should be one of four decisions: OPTIMIZE CURRENT WAN / PILOT SD-WAN / EXPAND TOWARD SASE / INVESTIGATE FURTHER. This keeps modernization tied to a real business or operational problem rather than a technology trend.
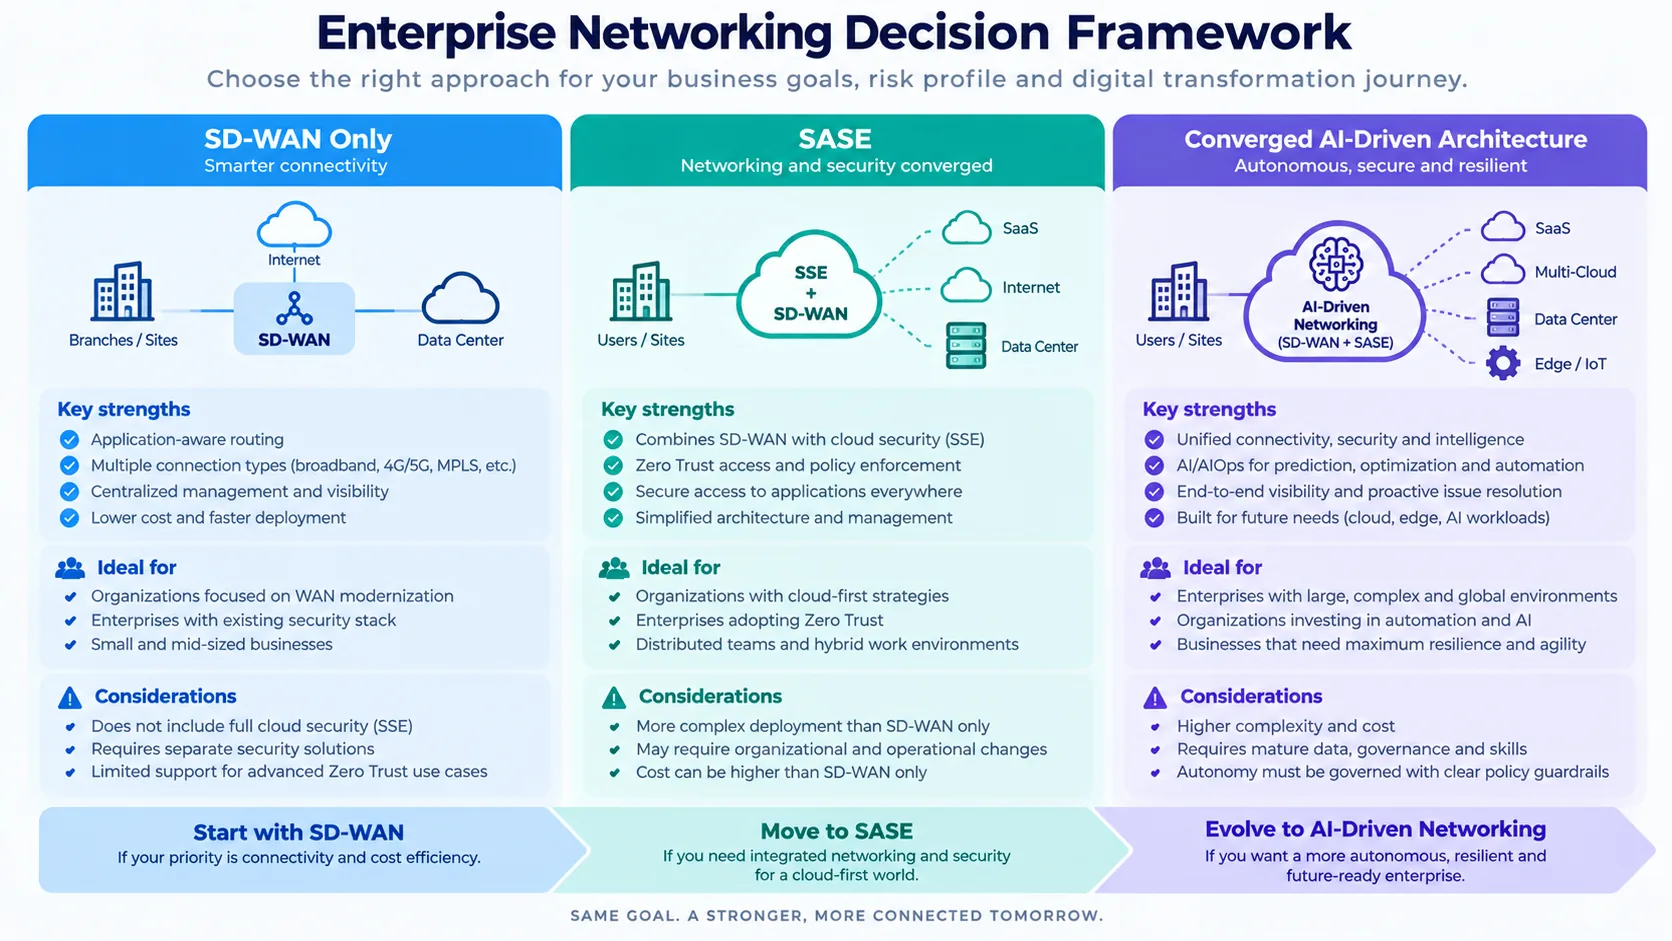
If your organization is earlier in its modernization journey and hasn’t yet made the jump from legacy WAN to modern SD-WAN, our guide on the advantages of next-generation SD-WAN over legacy solutions is a useful starting point before tackling the fuller SASE conversation.
What Comes After SASE? Autonomous and Agentic Networking
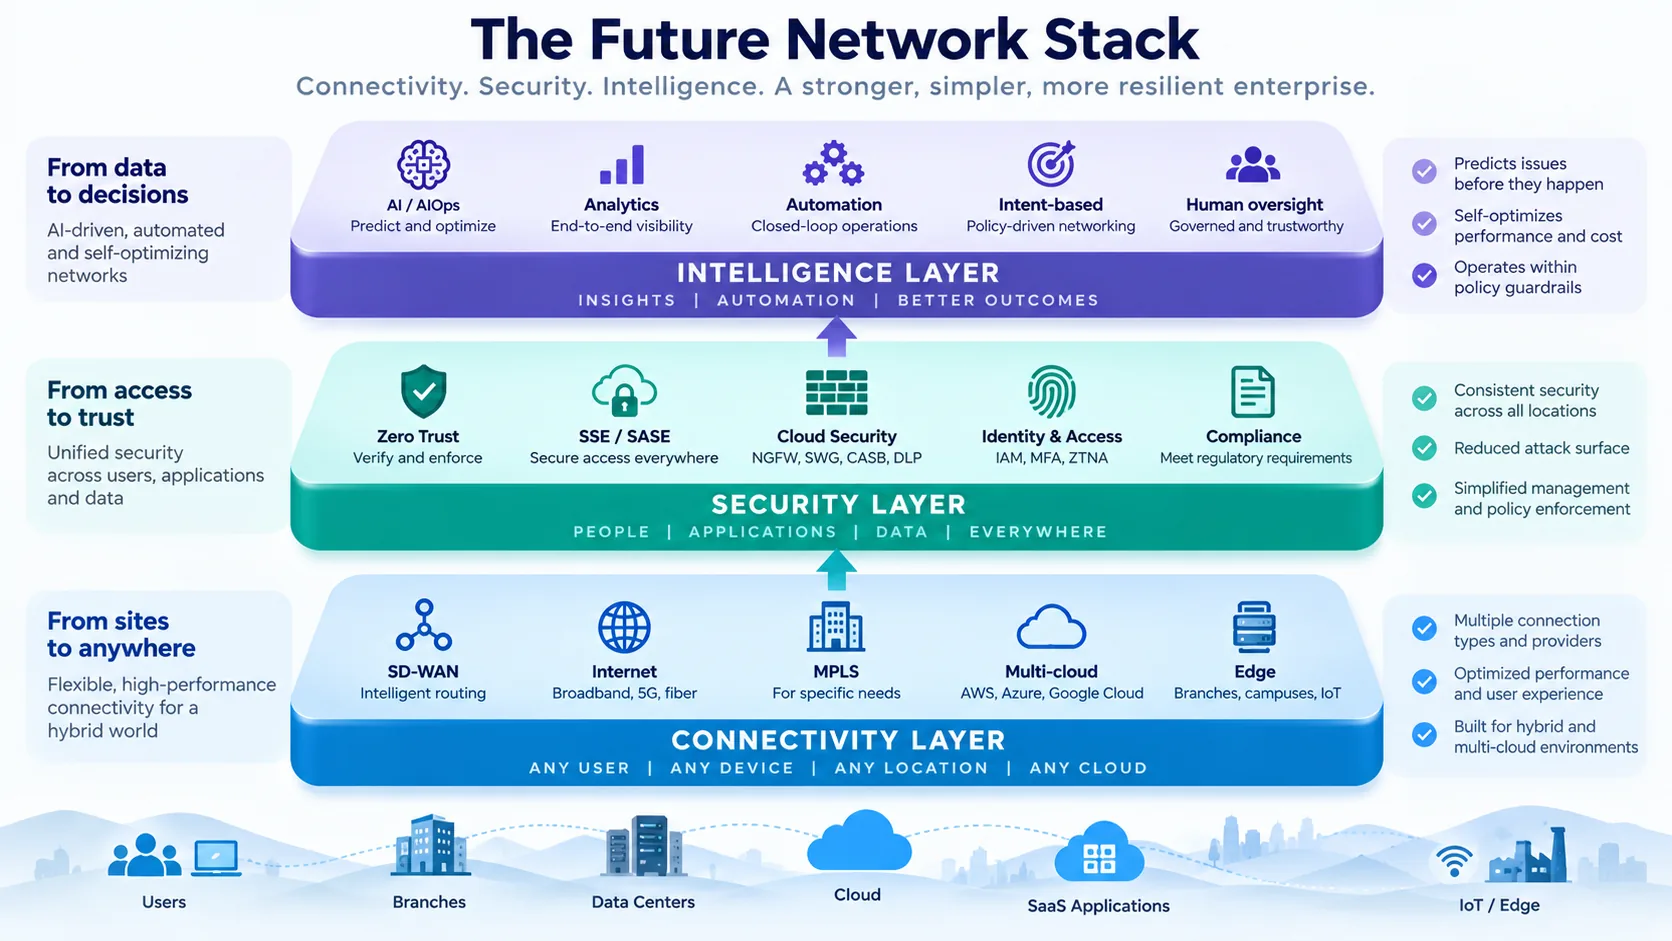
SASE converged networking and security. The next shift is toward more autonomous operations. These systems can detect conditions and recommend changes. In tightly governed scenarios, they can also execute predefined remediation or policy actions. The key is closed-loop automation with guardrails, not unrestricted autonomy. Organizations can gain speed while keeping policy, observability, rollback, and human accountability in place.
This connects to the broader agentic AI movement across enterprise IT. AI agents increasingly handle multi-step tasks instead of only suggesting actions. Our Agentic AI guide explores this shift in more depth. The same pattern applies to networking. Routine decisions may require less human intervention, while humans provide more oversight of the systems acting at scale.
This does not mean network engineers become unnecessary. Their role shifts away from manually executing routine changes. More time moves toward supervising and tuning automated systems. Organizations should treat this as a skills evolution, not simply a headcount reduction opportunity. Teams that invest early can build stronger hybrid expertise. Engineers who understand both network architecture and autonomous tooling are likely to become more valuable as these systems mature.
How Enterprise Networking Fits Into the Bigger Digital Transformation Picture
SASE and AI-driven networking rarely arrive as isolated IT projects. They connect to broader modernization across cybersecurity, cloud infrastructure, and IT operations. Much of that modernization also relies on virtualized network infrastructure. Our NFV guide and VNF vs CNF guide explain those software-based foundations in more detail. These technologies increasingly support the environments where SD-WAN and SASE operate.
Enterprise networking modernization works best when it connects to adjacent transformation efforts. Treating each initiative in isolation can create gaps. Companies should plan SASE alongside broader cloud and security modernization. This helps avoid a flexible network sitting beneath outdated operating models. Coordinated planning can also reduce redundant tools. It often creates a more consistent experience for the people using the network every day.
Conclusion: The Future of Enterprise Networking
SD-WAN solved connectivity. SASE combined that connectivity with cloud-delivered security. This closed gaps left by fragmented point products. AI now adds an intelligence layer on top. It can accelerate routing decisions, spot unusual threats, and automate routine operational tasks.
The future of enterprise networking is not a single product you buy once and forget. It is a converged, adaptive architecture that keeps evolving. That evolution follows how work changes and how AI workloads reshape traffic patterns. Organizations should treat networking as an ongoing capability to build. This usually delivers more value than a one-time technology purchase. Delaying modernization can also carry unnecessary cost and risk forward. Over time, that can make the eventual transition harder to justify and execute.
Frequently Asked Questions
Is SASE replacing SD-WAN? No. SASE doesn’t replace SD-WAN; it extends it. SD-WAN remains the networking foundation inside a SASE architecture, now converged with a full stack of cloud-delivered security services.
What is the difference between SASE and SSE? SSE (Security Service Edge) refers to the security half of SASE, including SWG, CASB, and ZTNA. SASE is the fuller architecture, combining SSE with SD-WAN’s networking capabilities into one converged system.
Do I need a single-vendor SASE solution? Not necessarily. Single-vendor SASE can reduce complexity, cost, and latency. Multi-vendor approaches offer more flexibility and product choice. The right model depends on your team’s tolerance for integration complexity and its need for specialized tools.
How does AI actually improve enterprise networking? AI can improve path selection and predictive analytics. It can also support faster threat detection across distributed traffic. Another use is application-aware prioritization for latency-sensitive workloads.
How long does a SASE migration take? There is no universal timeline. Duration depends on estate size, security scope, application dependencies, vendor architecture, and operating model. Larger organizations usually migrate in phases rather than through one cutover.
Is SD-WAN still relevant if I adopt SASE? Yes. SD-WAN remains a core, essential component of SASE. Adopting SASE doesn’t mean abandoning SD-WAN; it means running SD-WAN as part of a larger, security-converged architecture.
What industries benefit most from SASE and AI-driven networking? Organizations with distributed workforces often see strong benefits. The same is true for heavy cloud users and regulated industries. Common examples include financial services, healthcare, and branch-heavy retail.
Continue Learning
Continue exploring the TechTeamSynergy enterprise networking and SASE cluster with these related guides.
Comments are closed.