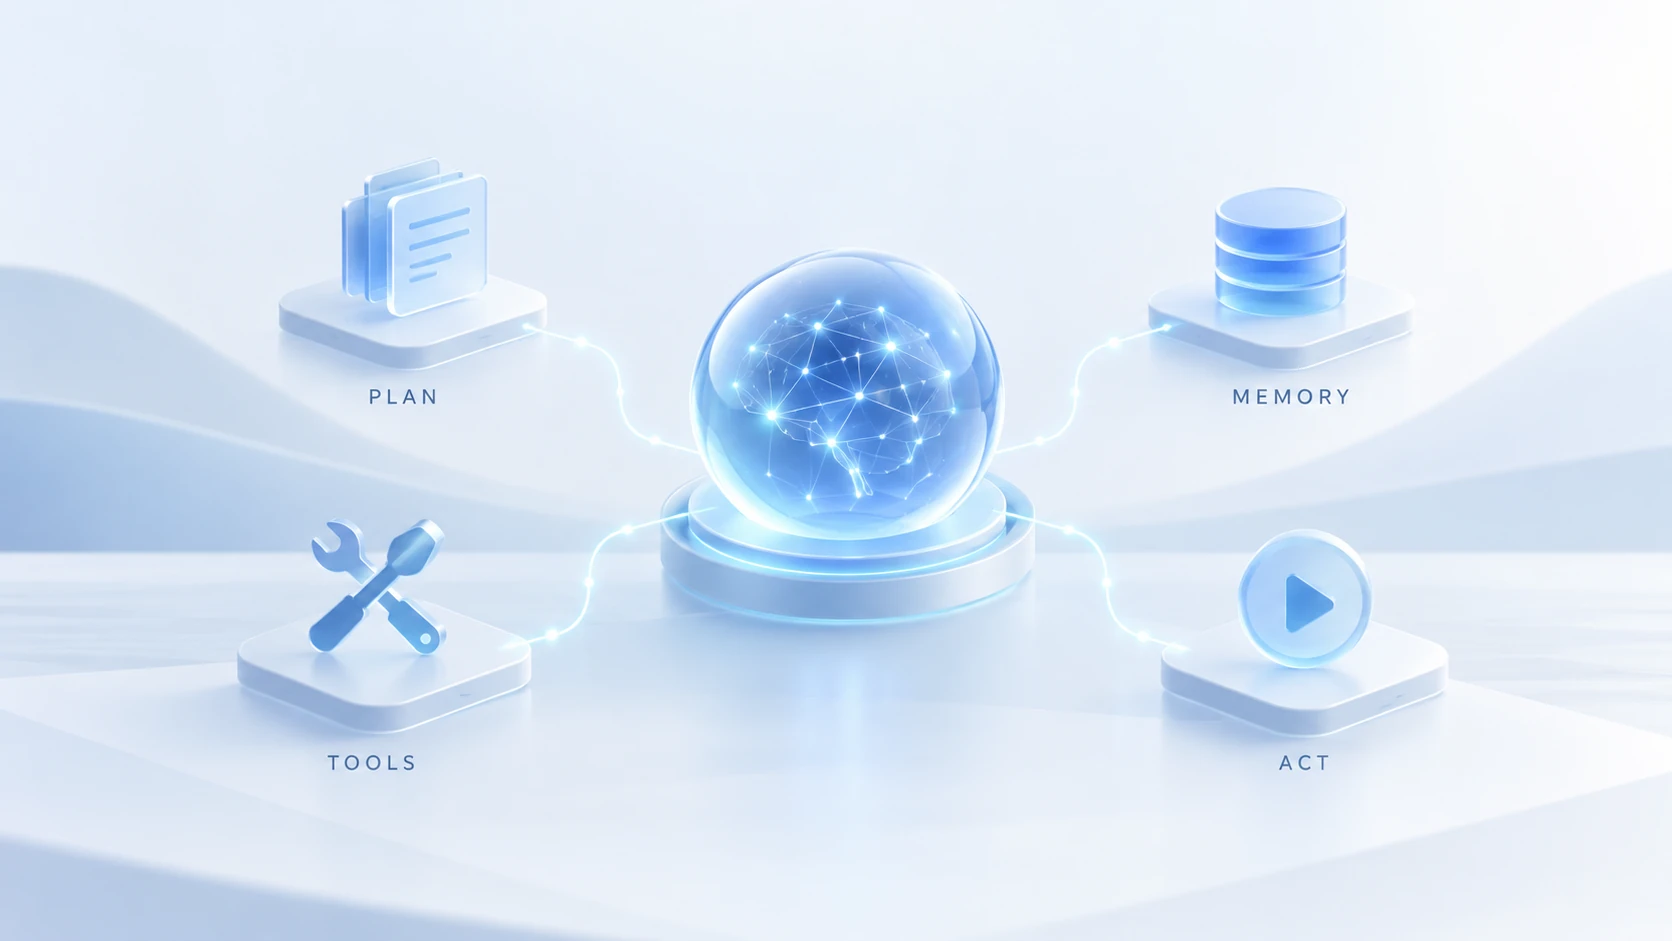
What is Agentic AI? Agentic AI refers to artificial intelligence systems designed to pursue goals by planning tasks, making decisions, using authorized tools and taking actions with a degree of autonomy.
This represents an important development beyond AI systems that primarily generate a response to a single prompt.
A conventional generative AI interaction might look like:
User Prompt → AI Generates Response → User Takes Action
An AI agent can operate more like:
Goal → Plan → Select Tools → Act → Observe Results → Adjust → Continue
This ability to perform multi-step tasks creates significant opportunities for automation, software development, customer operations, research and enterprise workflows.
It also introduces important questions about reliability, identity, permissions, cybersecurity, accountability and human oversight.
Agentic systems are part of the broader evolution of artificial intelligence. Unlike conventional generative systems that primarily produce content, AI agents can combine reasoning, tools and workflows to perform multi-step tasks.
This guide explains how Agentic AI works, how it differs from generative AI and traditional automation, the architecture of AI agents, enterprise use cases, benefits, limitations, security considerations and the future of autonomous AI systems.
Table of Contents
Jump directly to the section you need.
Understanding Agentic AI
Agentic systems are designed to do more than produce information.
They can potentially use information to determine and execute a sequence of actions toward a defined objective.
An agent may be able to:
- Interpret a goal
- Break the goal into smaller tasks
- Determine which actions are required
- Use authorized software tools
- Retrieve relevant information
- Execute parts of a workflow
- Observe results
- Adjust subsequent actions
The degree of autonomy can vary considerably.
Some systems merely recommend the next action to a human. Others can execute multiple steps automatically within predefined permissions and controls.
What Is an AI Agent?
An AI agent is a software system that can use information and algorithms to perform tasks on behalf of a user or another system.
An agent typically combines several capabilities rather than relying on a language model alone.
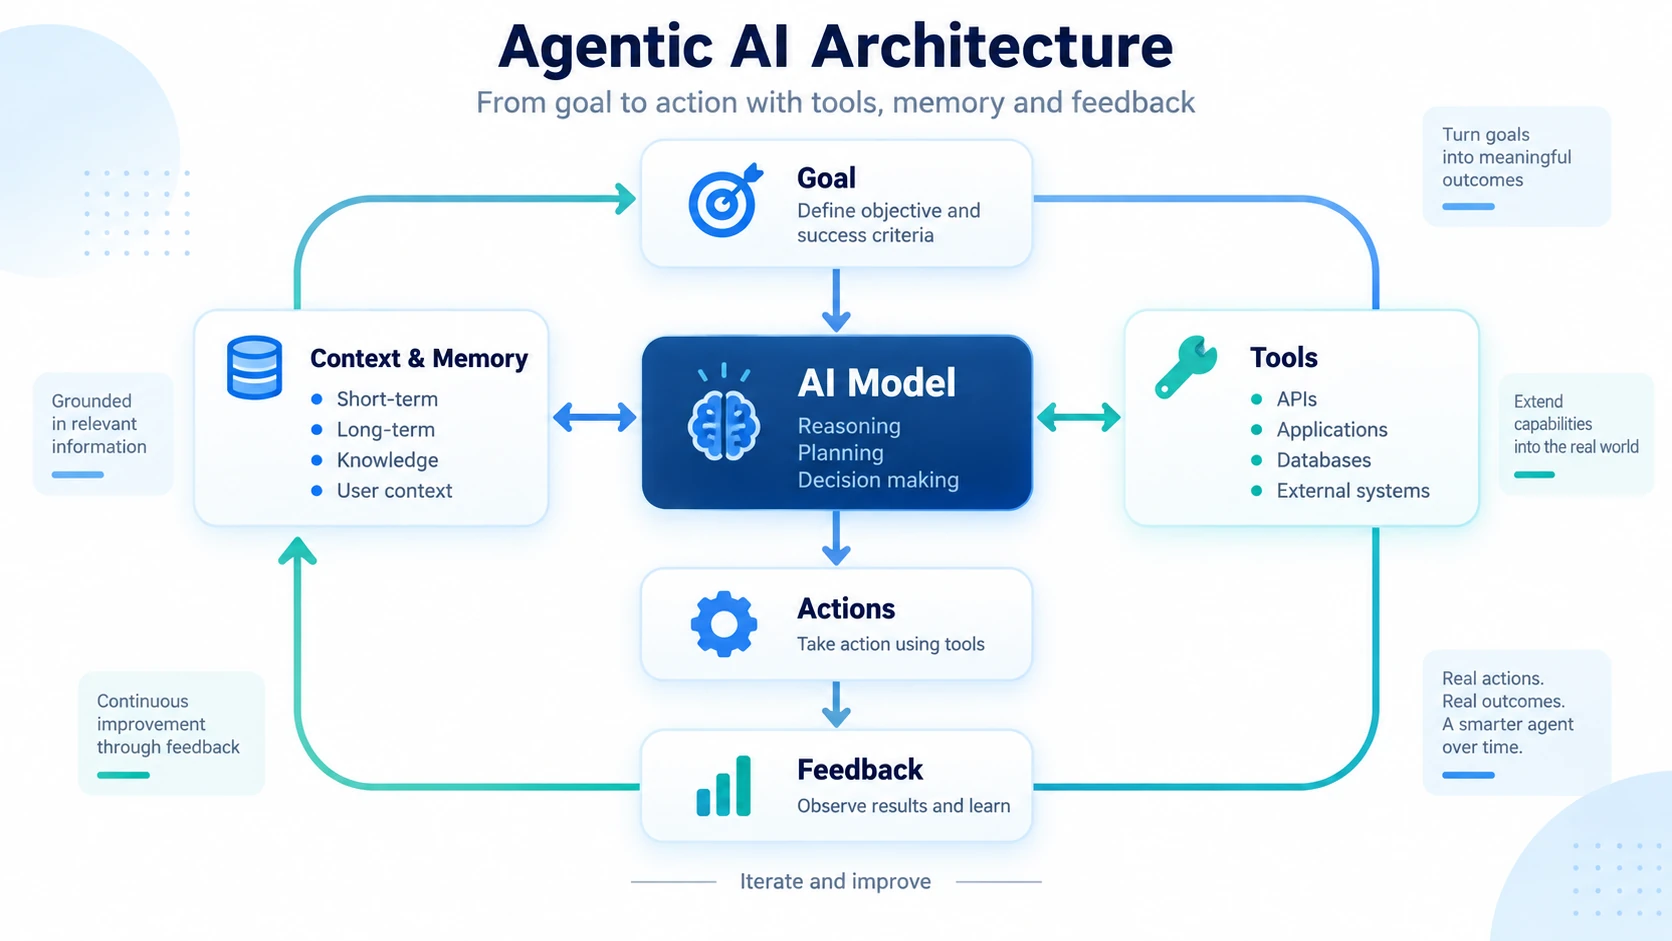
A simplified architecture is:
Goal + AI Model + Context + Memory + Tools + Permissions + Feedback
These components allow the system to move from generating information toward performing actions.
AI agents are also becoming an important area for standards, security and interoperability. The NIST AI Agent Standards Initiative focuses on enabling secure, interoperable and trustworthy AI agents across different systems and applications.
How Does Agentic AI Work?
There is no single universal architecture for every agent.
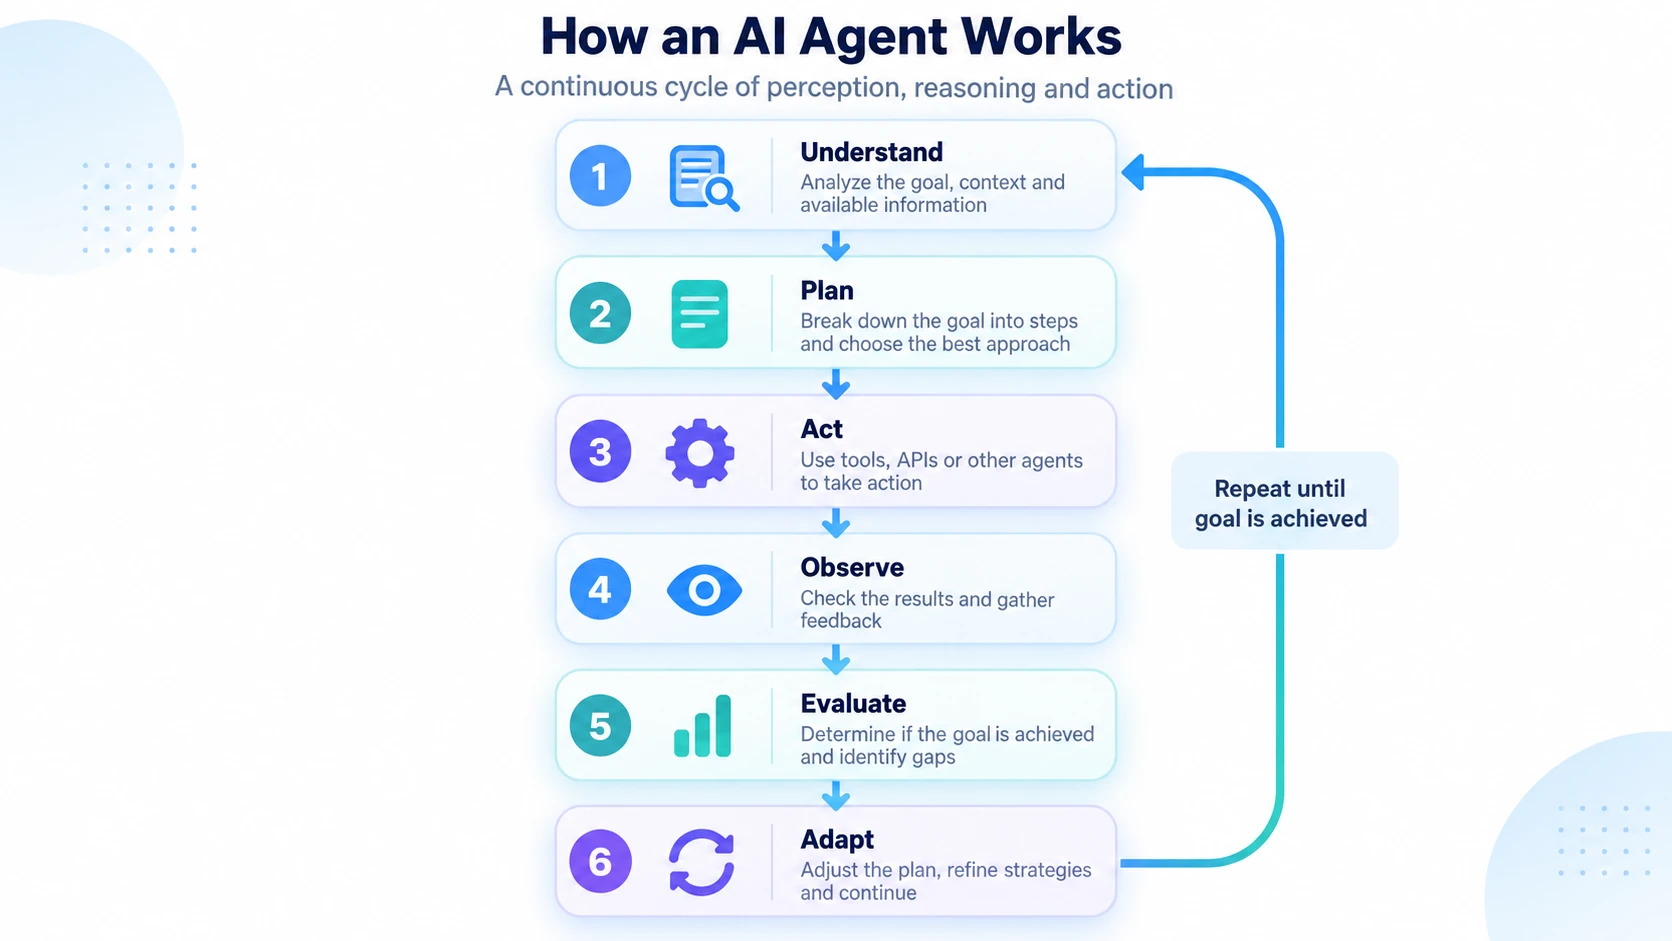
However, many systems follow a recurring cycle:
Understand → Plan → Act → Observe → Evaluate → Adapt
1. Receive a goal
The process begins with an objective.
For example, a business user might ask an authorized agent to summarize a collection of documents and prepare a draft report based on them.
2. Understand the context
The system evaluates the request along with available information, instructions and constraints.
3. Develop a plan
Rather than treating the request as one operation, the agent can divide it into multiple tasks.
For example:
- Locate relevant documents
- Extract the required information
- Compare the findings
- Prepare a summary
- Generate a draft report
4. Select an appropriate tool
If the system has been given access to approved tools, it can determine which one is appropriate for the next step.
Tools could include enterprise applications, databases, search systems, calendars, document repositories or workflow services.
5. Perform an authorized action
The agent uses the selected capability within the permissions assigned to it.
6. Observe the result
The system evaluates what happened after the action.
The result becomes additional context for the next step.
7. Adapt the plan
If the result differs from what was expected, the agent may revise subsequent steps rather than blindly continuing with the original sequence.
8. Continue or request human input
The system continues until the goal is reached, a predefined limit is reached, or human intervention is required.
Agentic AI vs Generative AI
Generative and agentic systems are closely related, but they should not be treated as synonyms.
| Capability | Generative AI | Agentic AI |
|---|---|---|
| Primary purpose | Generate content or responses | Pursue goals and perform tasks |
| Typical interaction | Prompt → Response | Goal → Multiple actions |
| Planning | May be limited to response generation | Can support multi-step planning |
| Tool use | Optional | Often central to useful agent workflows |
| Environment feedback | Usually limited | Can observe results and adjust |
| Autonomy | Usually lower | Can be higher within defined boundaries |
Generative models can therefore be important components of agents without every generative application being agentic.
Agentic AI vs Traditional Automation
Traditional automation typically follows explicitly designed workflows.
For example:
If Condition A → Execute Action B
Agentic systems can introduce more flexible decision-making:
Goal → Analyze Situation → Select Action → Execute → Evaluate Result
This can make workflows more adaptable, but flexibility also creates additional uncertainty and governance requirements.
Traditional automation remains preferable for many predictable, deterministic and highly controlled processes.
Agentic AI vs Chatbots
A chatbot primarily provides a conversational interface.
It may answer questions or generate content without taking actions in external systems.
An agent can potentially go further by interacting with authorized tools and applications.
For example, there is a meaningful difference between:
“Here is a draft of the meeting agenda.”
and:
“I created the draft agenda, checked the approved calendar information and prepared the requested meeting materials.”
The second scenario requires controlled access to external capabilities rather than language generation alone.
Core Components of an AI Agent
AI model
The model provides capabilities such as language understanding, reasoning support, classification or generation.
Instructions and goals
The system needs a clear understanding of what it is expected and permitted to accomplish.
Clear instructions remain important when working with autonomous systems. Our AI prompting guide explains how context, instructions and constraints can improve interactions with AI systems.
Context
Context can include the current task, available information, user instructions and relevant environmental state.
Memory
Some agents maintain information from previous steps or interactions.
Memory can improve continuity but creates additional considerations around accuracy, privacy and data retention.
Tools
Tools allow an agent to interact with systems outside the model itself.
Examples include:
- Databases
- Document repositories
- Enterprise applications
- Search services
- Business APIs
- Workflow platforms
Permissions
Permissions determine what the agent is authorized to access and what actions it may perform.
This becomes particularly important when an agent can modify information or trigger business processes.
Feedback
The agent needs information about the results of previous actions so it can determine what to do next.
What Is Tool Use in Agentic AI?
Tool use is one of the capabilities that distinguishes many agents from standalone language models.
The model itself may not contain the information or functionality required to complete a task.
Instead, an agent can be connected to authorized external capabilities.
A simplified flow is:
User Goal → Agent → Select Tool → Tool Executes → Result Returned → Agent Continues
This significantly increases what an AI system can accomplish, but it also increases the importance of access control and monitoring.
What Is Agent Memory?
Memory allows a system to retain information relevant to its task or interactions.
Different implementations can maintain information for different periods and purposes.
Memory might include:
- Previous task steps
- User-approved preferences
- Intermediate results
- Relevant workflow state
Organizations should carefully consider what information is retained, for how long, who can access it and whether it remains accurate.
Single-Agent vs Multi-Agent Systems
Not every agentic architecture relies on one agent.
Single-agent systems
A single agent coordinates the complete task and uses the tools available to it.
This can simplify architecture and governance.
Multi-agent systems
A multi-agent architecture assigns different responsibilities to multiple agents.
For example:
Coordinator → Research Agent → Analysis Agent → Review Agent
Specialization can be useful for complex workflows, but additional agents also introduce more communication, coordination, evaluation and security requirements.
Human-in-the-Loop Agentic AI
Autonomy does not have to mean removing people from a process.
A practical enterprise architecture can deliberately require human approval at important points.
For example:
Agent Plans → Agent Prepares Action → Human Approves → System Executes
Human approval can be particularly valuable for actions involving significant financial, operational, security or reputational consequences. For the broader team-design perspective, see how technology and teamwork can combine human judgment, digital tools and AI capabilities within a high-performing team.
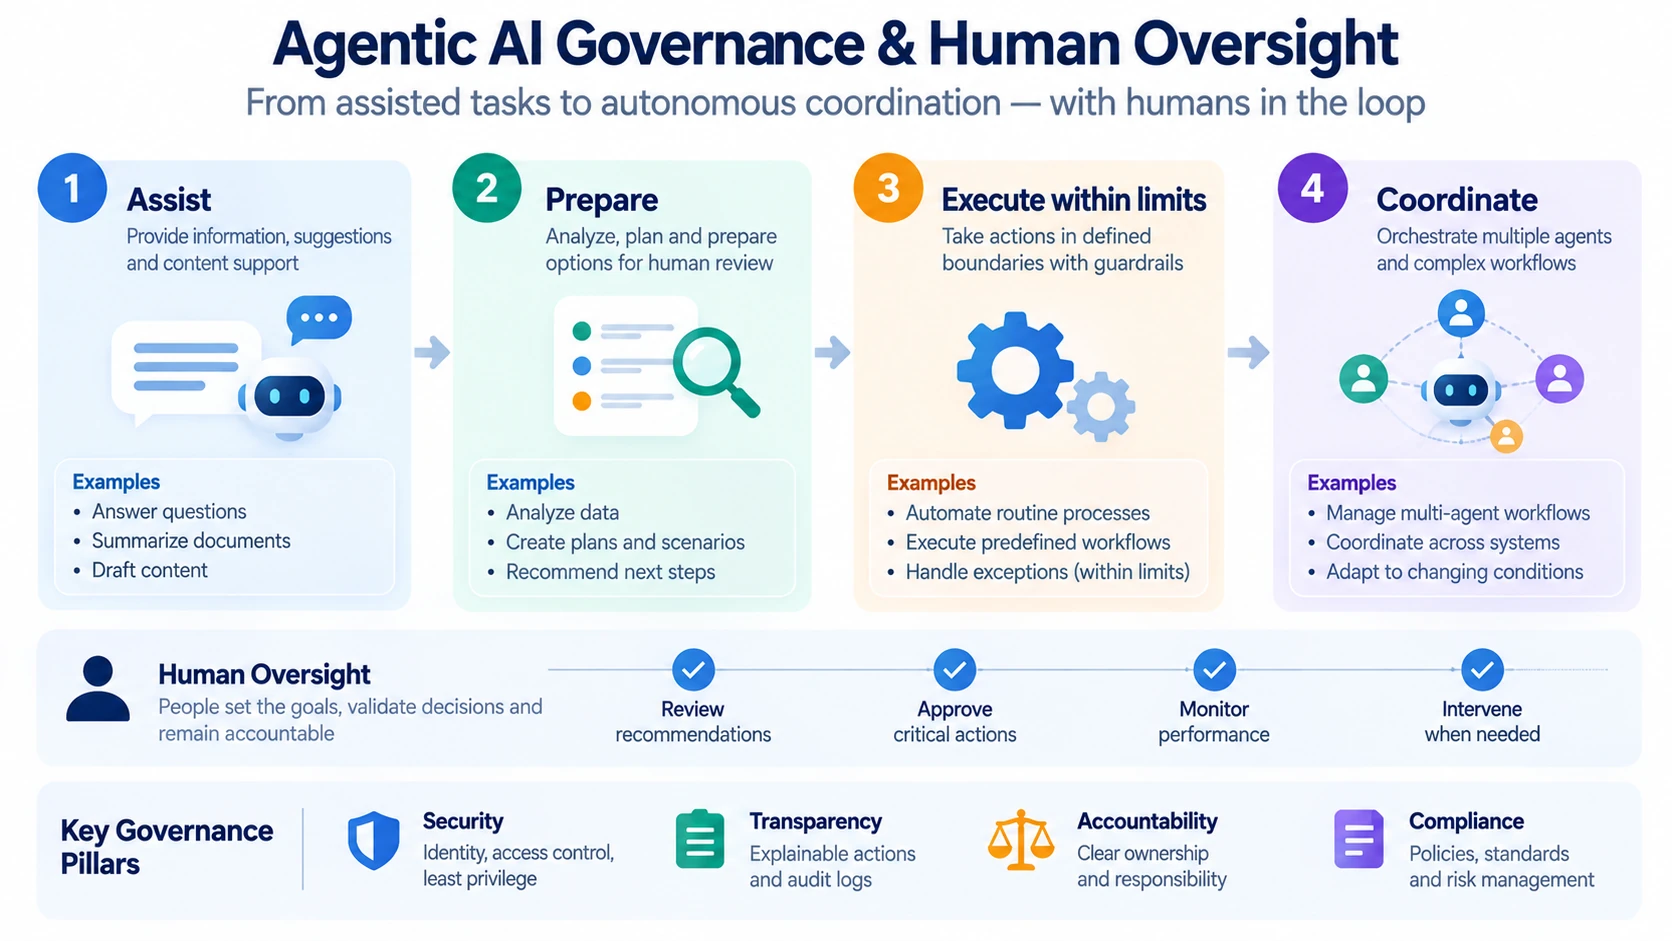
Levels of Agentic AI Autonomy
Agentic systems can operate with different levels of independence.
| Level | Example behavior |
|---|---|
| Assist | Recommend information or actions |
| Prepare | Create an action for human approval |
| Execute within limits | Perform predefined low-impact actions |
| Coordinate | Manage several authorized steps and tools |
Organizations do not need to maximize autonomy.
The appropriate level should depend on the task, reliability requirements and potential consequences.
Agentic AI Use Cases in the Enterprise
Knowledge work
Agents can potentially assist with multi-step tasks involving documents, research, summarization and information organization.
Customer service
An authorized system might retrieve customer information, summarize previous interactions and prepare recommended actions for an employee.
Software development
Agentic development systems can support activities such as analyzing requirements, preparing code changes, running approved tests and reviewing results.
Human review and established software-development practices remain important.
IT operations
Agents may assist operations teams by gathering diagnostic information, correlating events, summarizing incidents and recommending actions.
Cybersecurity
Security teams may use agents to help analyze security information, correlate events and support investigations.
Higher-impact security actions require particularly careful permissions, testing and oversight.
For a broader look at how intelligent systems support security operations, threat analysis and automation, read our guide to AI in cybersecurity.
Project management
Potential applications include:
- Collecting approved project information
- Preparing meeting summaries
- Organizing action items
- Drafting AI-assisted status reports
- Identifying dependencies
- Preparing risk information for review
Leadership, stakeholder management and accountability remain human responsibilities. For delivery teams and PMOs, AI governance for project managers and PMOs provides a practical way to define oversight, approval thresholds and decision rights.
For a practical human-in-the-loop approach to using AI for risk identification, analysis and continuous monitoring, see our AI-assisted project risk management guide.
AI agents are also beginning to support complex professional workflows such as AI in project management, where they can help collect updates, analyze risks and prepare project information for human review. For a practical comparison of today’s AI tools for project managers, see our use-case guide.
As agents take on more multi-step coordination work, a related question is whether increasingly autonomous AI could replace project managers or instead redesign how the role operates.
For a more immediate application of generative AI in day-to-day project work, explore these AI prompts for project managers covering planning, risks, reporting, meetings and project governance.
Enterprise networking
Network teams could use agents to assist with information gathering, operational analysis, documentation and troubleshooting workflows.
Changes to production infrastructure should remain subject to appropriate validation, authorization and operational controls. This is especially important when agentic systems influence AI-native Telco Cloud operations.
Benefits of Agentic AI for Organizations
Multi-step automation
Agents can coordinate tasks that previously required users to move manually between several applications.
Productivity
Routine information gathering and workflow coordination can potentially require less manual effort.
Adaptability
Agents can respond to changing information rather than following only one rigid sequence.
Natural-language interaction
Users can potentially express goals in natural language while the system determines which authorized capabilities are required.
Integration
Agents can act as an orchestration layer across existing applications and services.
Why Agentic AI Is More Difficult Than a Chatbot
A wrong chatbot answer can be inconvenient.
A wrong autonomous action can have a larger operational impact.
This changes the risk model.
Organizations need to consider not only:
“Did the model generate the right answer?”
but also:
“Did the system take the correct action, using the correct authority, in the correct context?”
Agentic AI Reliability Challenges
Agentic workflows can contain multiple dependent steps.
An error early in a process can affect later actions.
Potential challenges include:
- Incorrect interpretation of a goal
- Weak planning
- Incorrect tool selection
- Unexpected tool results
- Incomplete context
- Model errors
- Failure to stop when intervention is needed
Testing should therefore evaluate complete workflows rather than only individual model responses.
Agentic AI Security and Identity
Security becomes particularly important when agents can access enterprise systems.
An organization should be able to answer questions such as:
- Which agent is requesting access?
- On whose behalf is it acting?
- What information can it access?
- Which actions can it perform?
- How long does that authority last?
- How are its actions logged?
- How can its access be revoked?
Agent identity and authorization are therefore becoming important areas of enterprise architecture.
Identity and authorization are especially important when agents interact with enterprise applications and data. NIST is actively examining AI agent identity and authorization, including how organizations can authenticate agents, control their permissions and audit their actions.
Security guidance is also evolving specifically for autonomous and multi-step agent workflows. The OWASP Agentic AI Security Initiative provides research and practical guidance on risks such as agent control, tool access, memory and context, and secure Model Context Protocol (MCP) implementations.
Least Privilege for AI Agents
An agent should not automatically receive every permission available to the user or application that created it.
A safer design principle is:
Give the agent only the access required for its defined task.
This is an application of the established security principle of least privilege.
Permissions can also be limited according to:
- Task
- Resource
- Action
- Time
- Environment
Monitoring and Auditability
Organizations should be able to understand what important actions an agent performed.
Depending on the use case, useful records may include:
- Agent identity
- User or service represented
- Tools accessed
- Actions requested
- Actions executed
- Approvals
- Results
- Errors
Logging and monitoring support troubleshooting, governance and accountability.
Human Oversight for Agentic AI
Human oversight should be designed according to the potential impact of the task.
Low-impact activities may require less intervention.
Higher-impact actions may require explicit approval.
A useful principle is:
The greater the potential consequence, the stronger the validation and oversight should be.
Agentic AI Testing and Evaluation
Evaluating an agent requires more than measuring the quality of generated text.
Organizations may need to evaluate:
- Goal completion
- Planning quality
- Tool selection
- Action correctness
- Permission compliance
- Reliability across multiple steps
- Ability to handle unexpected situations
- Human-intervention behavior
Testing should reflect the real environment and intended use of the system.
Agentic AI Governance
Organizations adopting agents should establish governance before granting significant autonomy.
Governance can define:
- Approved use cases
- Permitted tools
- Access-control requirements
- Data policies
- Testing requirements
- Human approval points
- Monitoring
- Incident procedures
- Ownership and accountability
How to Adopt Agentic AI in an Enterprise
1. Choose a bounded use case
Start with a specific workflow rather than attempting unrestricted autonomy.
2. Define the goal
Specify what the agent should accomplish and what is outside its responsibility.
3. Identify required tools
Give access only to systems needed for the workflow.
4. Define permissions
Apply least privilege and avoid unnecessary access.
5. Establish human checkpoints
Determine which actions require approval.
6. Test complete workflows
Evaluate normal scenarios as well as unexpected conditions.
7. Monitor actions
Maintain appropriate visibility into important agent activity.
8. Measure outcomes
Determine whether the system actually improves productivity, quality or another defined objective.
9. Expand gradually
Increase capabilities or autonomy only when evidence supports doing so.
How to Measure Agentic AI Success
Organizations should measure business outcomes rather than simply counting how many agents they deploy.
Useful measures might include:
- Task completion rate
- Time saved
- Quality
- Error rate
- Human intervention rate
- Cost per completed task
- User satisfaction
- Reliability
- Policy compliance
Common Agentic AI Implementation Mistakes
Giving too much autonomy too quickly
Organizations can begin with assistance and approval-based workflows before expanding autonomy.
Giving agents excessive permissions
Access should match the actual task.
Evaluating only the underlying model
The complete system—including tools, permissions, workflows and integrations—needs evaluation.
Ignoring failure scenarios
Teams should define what happens when information is missing, tools fail or the agent is uncertain.
Removing humans from every workflow
The objective should be appropriate automation, not maximum autonomy.
Ignoring accountability
Organizations need clear ownership for deployed systems and their permitted actions.
The Future of Agentic AI
Agentic systems are likely to become increasingly integrated into enterprise software and digital workflows.
Several developments will be particularly important.
Agent Interoperability: MCP, A2A and Emerging Standards
Interoperability is becoming a central part of agentic AI architecture. The Model Context Protocol (MCP) provides a standardized way for AI systems to connect with tools, data and services, while the Agent2Agent (A2A) Protocol focuses on communication and coordination between agents.
These approaches can reduce custom integration work and make it easier to build agent ecosystems across applications, vendors and specialized services. They also increase the importance of authentication, authorization, secure tool access and consistent governance across agent boundaries.
Stronger identity
Organizations will need reliable ways to identify agents and determine what authority they have.
More specialized agents
Rather than one agent performing every task, enterprises may use specialized systems for particular domains and workflows.
Multi-agent orchestration
Multiple specialized agents may coordinate to complete complex processes.
Improved evaluation
Testing will increasingly need to measure complete agent behavior and real-world outcomes rather than only model performance.
More controlled autonomy
Enterprise adoption is likely to depend on systems that combine useful autonomy with permissions, monitoring and human oversight.
Frequently Asked Questions About Agentic AI
What is Agentic AI in simple terms?
Agentic AI refers to systems that can pursue goals through multiple steps, potentially planning tasks, using authorized tools, taking actions and adjusting based on results.
What is an AI agent?
An AI agent is a software system that uses information and algorithms to perform tasks on behalf of a user or another system.
Is Agentic AI the same as generative AI?
No. Generative systems primarily create content or responses. Agentic systems can use generative models while adding planning, tool use, actions and feedback loops.
Is an AI chatbot an agent?
Not necessarily. A chatbot that only generates conversational responses may not be agentic. An agent generally has additional capabilities to pursue goals or interact with external tools.
Can AI agents use software tools?
Yes. Tool use is a common capability in agent architectures. Tools can provide access to approved databases, applications, search services and workflows.
Can multiple AI agents work together?
Yes. Multi-agent systems can assign different responsibilities to specialized agents, although this increases coordination and governance complexity.
Are AI agents fully autonomous?
They do not have to be. Autonomy can range from recommendations and human-approved actions to more independent execution within predefined limits.
What are the main Agentic AI risks?
Risks can include incorrect actions, excessive permissions, unreliable multi-step behavior, privacy problems, security issues and insufficient oversight.
Do AI agents need human oversight?
The appropriate level depends on the task and potential impact. Higher-impact actions generally justify stronger validation and human control.
How should companies start using AI agents?
Begin with a bounded workflow, define clear permissions and success criteria, establish human checkpoints, test the complete process and expand gradually based on measured results.
Conclusion
Agentic AI moves artificial intelligence from primarily generating information toward systems capable of pursuing goals and performing multi-step tasks.
A useful model is:
Goal → Plan → Tools → Actions → Feedback → Adaptation
This can create significant opportunities for enterprise automation, software development, operations, customer service and knowledge work.
But greater autonomy also creates greater responsibility.
Organizations need to consider identity, authorization, least privilege, testing, monitoring, human oversight and accountability before allowing agents to perform important actions.
The future of enterprise Agentic AI is therefore unlikely to be defined simply by maximum autonomy.
It will be defined by the ability to combine useful autonomy with reliable controls, measurable value and responsible human oversight.
Strong agentic-AI workflows still depend on clear instructions, reliable tool use and human verification. For a practical foundation in prompting, coding, APIs and automation, explore ChatGPT Unlocked.
Continue Learning
Explore these related TechTeamSynergy guides to deepen your understanding of AI, automation and practical enterprise adoption.
Comments are closed.